Turning on multi-factor authentication is one of the highest-value steps a household can take. It stops the majority of account-takeover attempts that rely on stolen passwords alone. Yet many families enable MFA, lose the second factor, and then spend days recovering access. The problem is not the technology. It is the missing recovery plan.
I have helped relatives and friends recover locked accounts more times than I can count. The pattern is almost always the same: the authenticator app was on a phone that was replaced, the recovery codes were never printed, and the backup email was itself protected by the same broken MFA. The following process avoids that cycle. It prioritizes the accounts that matter most and builds recovery into the setup from the first day.
Choosing Where to Start
Protect the email account that resets everything else
Most account recoveries flow through email. If the primary email is taken over, the attacker can reset passwords on banking, shopping, and social accounts. Enable MFA on the main email first and confirm that recovery options are solid before moving to other services.
Next secure financial and payment accounts
Banks, credit-card issuers, and major payment services should follow immediately after email. These accounts often support stronger methods such as authenticator apps or hardware keys. Completing them early reduces the damage if a password is later compromised elsewhere.
Add the accounts used for identity or government services
Tax accounts, Social Security portals, and similar services hold sensitive personal data. Once email and financial accounts are protected, these become the next priority. Some still rely on SMS, so document the limitations and plan stronger methods when they become available.
Leave lower-risk accounts for a second pass
Streaming services, shopping sites with stored cards, and social accounts can wait until the critical layer is finished. Trying to secure everything in one evening leads to incomplete recovery planning. A staged approach keeps the work manageable and the recovery materials organized.
Selecting and Setting Up the Second Factor
Prefer authenticator apps over SMS when possible
SMS codes can be intercepted through SIM-swap attacks or phishing. Authenticator apps generate codes on the device and are harder to redirect. Install a reputable authenticator on the primary phone and, if practical, on a second device belonging to another adult.
Register at least one backup method during setup
Most services allow a secondary phone number, a backup authenticator, or a set of one-time recovery codes. Register the backup while the primary method is still fresh. Waiting until after a lockout makes the process far more difficult.
Print or write the recovery codes and store them offline
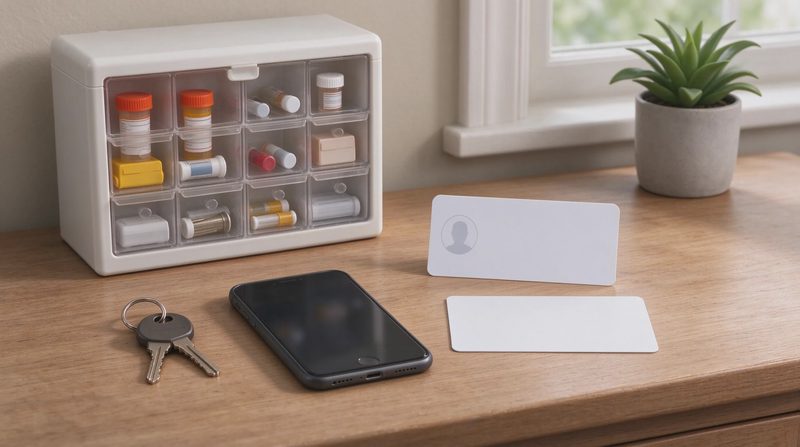
Recovery codes are single-use strings that bypass the normal second factor. Print them or write them clearly and store the paper in a secure household location. Digital-only storage of recovery codes recreates the same single-point-of-failure problem the codes are meant to solve.
Test the new MFA method before leaving the setup screen
After enabling MFA, log out and log back in once to confirm the code works. Then test the recovery path if the service allows it. A five-minute test during setup prevents hours of frustration later.
Building Recovery Paths That Survive Device Loss
Designate a second adult who can complete recovery
In a household with two adults, each should be able to help the other regain access. Share the location of recovery codes and the process for requesting emergency access. Solo recovery plans fail when the only person who knows the system is unavailable.
Keep recovery codes in more than one physical place
A single envelope in a drawer is better than nothing, yet a second copy in a different location protects against fire, move, or simple misplacement. The codes themselves are static, so duplication does not create new risk if the locations remain private.
Update recovery information when phones or numbers change
Replacing a phone or changing a mobile number is a common moment for MFA to break. Before retiring the old device, transfer authenticator entries and confirm that backup numbers still work. A short checklist at phone-upgrade time prevents most lockouts.
Avoid relying solely on a single email for all recoveries
If every account lists the same email as the recovery address, a problem with that email becomes a problem with everything. Where services allow a secondary recovery email or phone, add one. Diversity in recovery channels increases resilience.
Common Mistakes That Create Lockouts
Enabling MFA without saving recovery codes
Many people turn on the second factor, close the browser, and never print the codes. Months later the phone is lost and the account is unreachable. Saving the codes is not optional; it is part of the same setup session.
Storing authenticator apps only on one device
A single phone holding every authenticator entry creates a single point of failure. Where possible, register a second authenticator or keep printed codes current. Some managers also allow secure backup of authenticator seeds; use that feature if available.
Using SMS as the only second factor for high-value accounts
SMS is better than no MFA, yet it is the weakest common method. Move high-value accounts to authenticator apps or hardware keys when the service supports them. Leave SMS for accounts that offer no stronger option.
Forgetting to remove old devices from account settings
After a phone is replaced, the old device may still appear as a trusted MFA method. Remove it promptly. Lingering trusted devices can be used by anyone who later obtains the hardware.
Comparing MFA Methods for Household Use
Method | Strength | Ease of Daily Use | Recovery Difficulty if Lost | Best Use Case |
|---|---|---|---|---|
Authenticator app | High | High once set up | Medium (needs codes or second device) | Email, banking, primary accounts |
SMS codes | Medium | High | Low if number is active | Accounts that offer nothing stronger |
Hardware security key | Very high | Medium | High if key is lost without backup | Highest-value accounts for tech-comfortable users |
Recovery codes only | N/A (backup) | Low | Low if codes are stored | Essential companion to every other method |
This comparison helps households choose methods that match their comfort level while still raising the overall security baseline.
Maintaining MFA Across the Household
Review the list of protected accounts twice a year
A short checklist of the accounts that should have MFA keeps the system from drifting. New services appear, old ones are abandoned, and recovery contacts change. A twice-yearly review takes little time and prevents gaps.
Teach older children the same recovery discipline
Teenagers who manage their own email or school accounts should also save recovery codes and understand the backup process. The habits formed early reduce the chance of lockouts when they later handle more sensitive accounts.
Keep a simple written map of what protects what
A one-page note listing the primary email, the authenticator location, and where recovery codes are stored is enough. It does not need to contain the codes themselves—only the pointers. The map is useful when the primary adult is unavailable.
Accept that perfect coverage is less important than solid coverage of the critical layer
Not every low-risk account needs MFA on day one. Protecting email, financial services, and identity-related portals first delivers most of the benefit. Expanding outward from that core is sustainable; trying to secure everything at once is not.
No comments yet — be the first to share a thought.